Showing posts with label SCADA. Show all posts

Thursday, February 07, 2008

Why SCADA still is insecure

My friend Erik pointed me to this piece of information on the SCADA mailing list. A new SCADA security mailing list is in the works. This snippet is taken from the invitation mail sent to other mailing lists:
"Due to heightened security and awareness levels worldwide, ALL MESSAGES ARE WATCHED CAREFULLY.
Violators who report methods that are going to disable, damage, dismember, destroy, or disarm any control system,
SCADA device, or infrastructure will be reported to DHS (and/or their respective national or federal authority)."

Ex hacker-now-turned-to-tech-journalist Keving Poulsen, of wired magazine, had this remark:

"Only the SCADA community could conceive of a mailing list that tries to get you arrested for discussing security issues. And we wonder why SCADA is still insecure."


he might have a point there....

SCADA security in upcoming issue of IEEE Security & Privacy magazine

The very relevant and interesting IEEE Security & Privacy magazine will have the November/december issue focused on Process control security. The submission deadline is 4th of april of you would think of submitting an article.

See here for more information on the PCS IEEE issue.

Wednesday, February 06, 2008

The 2008 S4 Scada security conference


We recently atteded the S4 conference in Miami, USA, facilitated by Dale Peterson and the good people of Digital Bond. 

S4 is the SCADA Security Scientific Symphosium, a yearly event held in the end of january.

S4 is a rather small and intimate event that makes you feel that you are on the first row in the conference room and at the same time really have first hand access to the worlds technical expertise to the professionals in the SCADA Security arena. It is amazing to realize that there are only a few handful of people qualifying for that title.


The symposium had eight invited speakers, some very good, some less scientific or relevant. Both keynote speakers where really good. Day one Steve Lipner the Microsoft’s Senior Director of Security Engineering Strategy gave a talk on security with regards to systems and software development. If only SCADA vendors and other in the automation business would start to work according to this methods, things would certainly look a lot better.

Day two, Dave Aitel described the way a serious security researcher or a skilled attacker works when he (she?) reverse engineers executable code and proprietary and unpublished communications protocols. I just hope that this is the eye opener that many people really need. They all should know Shannons maxim and the Kerckhoff principle. The enemy knows the system. And the security should really depend on other factors that obscurity.

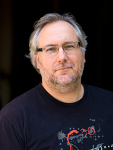
One of the better speakers with a really interesting topic, security in wireless systems, was Denis Foo Kune (depicted above) of Honeywell Research. His talk on ISA 100, Zigbee, WLAN and radio systems security was really nice.


For those of you not attending the symphosium, now there is a new opportunity for you to order the conference proceedings from Digital Bond.

According to Dale, Digital Bond plan to run S4 2009 again. The same dates and the same place. Mark your calendars.

Tuesday, May 29, 2007

New mailing list on SCADA security and IT/infosec in relation to Critical Infrastructure

I've started a mailing list on SCADA security "cyber security" and IT/infosec in relation to Critical Infrastructure. It is already a number of good, initiated, members from academia, vendors, users, government agencies, etc.

Drop me a note at rom * romab * com if you are interested to participate.

Friday, October 13, 2006

Process control networks and critical information infrastructure

Security in the societys information infrastructure or critical base infrastructure is a major concern these days. The reasons for this is, among other things:
  • The trend is that events that happens in the physical domain (e.g. sabotage, obstruction) also starts to happen in the electronical (often called "cyber") domain.
  • Many systems where designed long ago according to simple functional requirements, not to withstand a modern (potentially) hostile IT environment.
  • There is many people looking for new hot topics in the information security market....

    Anyway, this article can serve as a simple starting point for this topic

    The helpful people at UK's National Infrastructure Security Co-ordination Centre NISCC has produced quite some information in this area including best practise documents, architecture and design recommendations, etc.

    A good place to get fresh information on embedded systems security, process control systems security, etc. is the SCADA Security Blog hosted by Digital Bond. Not only do they have some nice information, they've also produced a number of tools that might be useful. Cisco's Critical Infrastructure Group (CIAG) is another interesting place with some information.

    SANS recently held a webcast on Cyber Attacks Against SCADA and Control Systems. Eric Byer talked about "his" ISID database on published incidents or attacks against process control systems and the sponsor Symantec talked some on their pen tests against process control systems. I have several problems with the ISID database:
  • The researchers draw a number of conclusions from a statistically limited number of incidents
  • The lack of publicly available information. I can live with fact that some data is hidden to protect the participating organizations, but the basic stuff - such as the definitions of "accidents", "incidents", etc, should be available for the
    data to be usable.
    I also have problems with not beeing able to get the research articles they've written on the subject.
    I've tried to get some info from Eric and others at BCIT. So far all I've got is bounced mail....

    DHS have released a report on the CyberStorm excercise, a large scale excercise with simulated attacks on critical infrastructure components. It describes, among other things, how important it is to get communication (oral, human communication) and trust working between involved parties during a crisis situation. In a context where you have a mix of govermental bodies, commercial entities and other organisations without established and trustworthy channels this might be a major problem. The excercise was done in the US, but I'd say that the conclusion is general and would be apropriate to most contries in the event of an attack against the critical infrastructure.

    Other, older, reports and documents of interest include:
  • The GOA has also released an interesting report called CRITICAL
    INFRASTRUCTURE PROTECTION -DHS Leadership Needed to Enhance Cybersecurity
    .
  • National infrastructure advisory council report on prioritizing cyber vulnerabilities
  • Friday, September 15, 2006

    The twilight zone

    I have developed a specific interest in the twilight zone between different aspects of security, where security and safety issues crosses, or where there are physical and logical security issues or differences between technical issues and psychological acceptance of security (even usability).

    Usability AND security (not OR) is the name of an excellent book edited by Lorrie Faith Cranor and Simson Garfinkel. They cover psychological acceptance of security, secure systems, privacy and anonymity systems, etc. One of the pioneers in the softer aspects of information security is Ka-Ping Yee with his Secure Interaction Design, SID, which contain some really good ideas and rule of thumb. He have provided some nice posters on the matter.

    Matt Blaze have written several excelent articles on this subject, including Safecracking for the Computer Scientist and Cryptology and Physical Security: Rights Amplification in Master-Keyed Mechanical Locks, where he applies modern ideas from computer science to attack traditional security systems. By performing his research he have received some critic from locksmiths and others. Hey, even Nobel laureate Richard Feynman is known to be a safe cracker!

    Another, similar type of interesting research where real-world security meets information security is the research performed by Ross Anderson on ATM machines in Why Cryptosystems fail, by Avi Rubin of Johns Hopkins and Ed Felen of Princeton on Electronic voting machines, etc.

    The last couple of years I've found Process Control Systems, SCADA and similar industrial applicactions of special interest, since it is an area where there security and safety meets (collide?). Another aspect of this collision is the cultural differences in the groups working, i.e. IT staff versus the staff working with process control. There are many security aspects in the industrial IT field that is simply different from traditional IT - scarce resources, unwillingness to change (upgrade software? no way!), and, many systems have a completely different life cycle. I will write more on this in coming articles.